





 Earn up to 50% APR
 Boost earnings with NFTs
 Play, HODL & earn more
🍵 Major Privacy Spill: Viral App “Tea” Leaks Users’ Private Data Despite Promising Anonymity
-
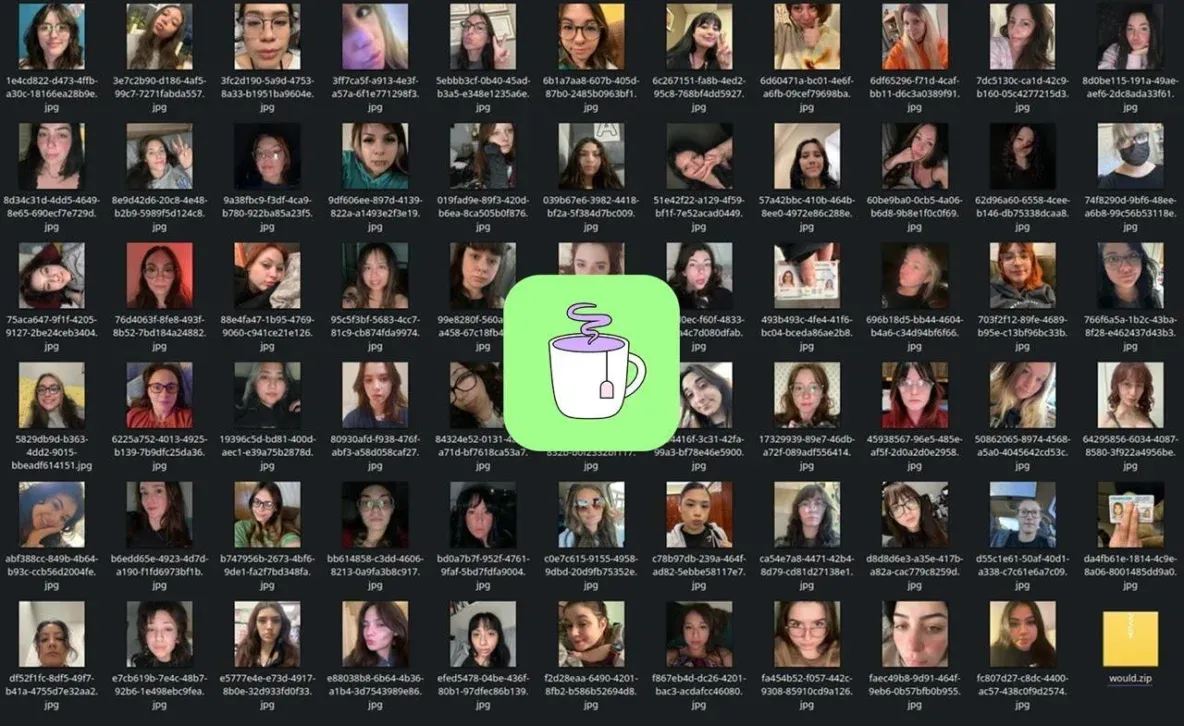
Tea Dating Advice — a viral app for anonymously sharing “red flags” about men — has made headlines not just for topping the App Store, but for a major data leak that exposed thousands of user identities.
What’s Tea?Tea is a gossip-style app where women anonymously report problematic behavior from men — think cheating, gaslighting, or narcissistic behavior. The app has surged in popularity this summer, becoming #1 in the US App Store. It even includes premium features, like alerts if someone else starts dating “your guy.” According to Sensor Tower, Tea was downloaded over 400,000 times in a month and earned more than $200,000 on iOS.Here’s the Spill…
 ️
On July 25, a user on 4chan revealed that 59 GB of user data — including selfies and driver’s licenses used for identity verification — were publicly accessible without a password via Firebase.
The files were not encrypted, and the link didn’t require login.

The leaked data was downloaded and briefly posted online.

This directly contradicts Tea’s branding as an anonymous and safe space.
Tea’s Response?
Tea’s team claimed the data came from an outdated Firebase system used before February 2024.

They admitted 72,000 images were exposed, including 13,000 selfies.

In a now-viral FAQ, they said the data was archived to comply with cyberbullying investigations and couldn’t be linked back to user accounts (though that’s being heavily questioned).
What’s the Lesson Here?
Even apps that promise anonymity and empowerment can compromise user trust when they fail to handle sensitive data securely. If you’re sharing personal information — even in the name of justice — know where it’s going and how it’s stored.
Would you use an “anonymous” dating intel app after a leak like this? Or is the tea just too hot to sip?


-
This incident is a major privacy crisis—and it hits especially hard given Tea’s promise to safeguard women’s data. Tea’s legacy Firebase storage system leaked approximately 72,000 user images, including 13,000 selfies and IDs used for identity verification, plus 59,000 images from posts and direct messages—all sourced before February 2024. The app’s claim that it was built to protect users has been painfully undermined. This raises serious concerns about app security and developer responsibility.
-
Tea was marketed as a safety-focused whisper network where anonymity and screenshots were blocked—but this breach betrays that promise. Users who joined before Feb 2024 had their images stored against company policy and scraped, soon appearing on forums like 4chan. Although the company claims no current data was exposed and is working with third-party cybersecurity teams, trust is eroded.This is now a broader discussion on how platforms with sensitive UGC must enforce proactive data deletion and security audits—not just hype assurances.